Artificial intelligence is reshaping cybersecurity. It changes how attackers operate and how defenders respond. Source: securityaffairs.com.
AI in Cybersecurity: A Double-Edged Sword
AI agents now automate routine tasks. They analyze large datasets and detect vulnerabilities.
Defenders use AI to spot threats faster. These tools process terabytes of logs and behavior data in real time.
AI-powered systems flag unusual login patterns or data exfiltration. These signs appear before breaches escalate.
Attackers also use AI to speed up operations. AI-driven attacks scale quickly and target systems with precision.
These attacks adapt to defenses in real time. They conduct reconnaissance and generate tailored payloads with little human input.
OpenAI Faces Scrutiny Over Data Practices
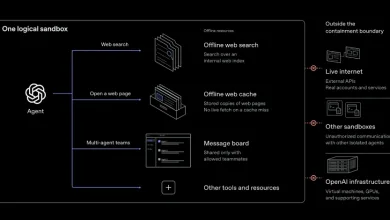
According to The Register, OpenAI claims it traced an ex-employee’s digital footprint.
The discovery involved 100-plus secret files. Internal records show data tracking mechanisms were used across corporate systems.
Security experts warn of privacy and data integrity risks. Such practices raise concerns about transparency and accountability.
AI training environments often handle sensitive data. Clearer rules are needed for how data is shared and used.
Meta Removes Language Linked to AI Training Concerns
Meta removed content from its Muse app. The content raised concerns about data scraping and AI training.
This change follows internal reviews and public feedback. It shows growing awareness of ethical AI risks.
downloads in 40 days. This milestone was hit by only 11 other apps.
The rapid adoption shows AI tools’ strong consumer appeal. It also highlights the need for responsible data practices.
AI-Driven Threats and Vulnerabilities
AI identified a critical flaw in web infrastructure.
The issue lies in common web server configurations. It allows remote code execution.
Another AI-driven campaign used the ARTEX tool. It compromised supply chains by targeting outdated software dependencies.
Supply Chain Attacks via AI
A nation-state campaign used AI to automate supply chain attacks.
Attackers exploited outdated software dependencies. They gained access through routine updates.
These attacks mimic normal maintenance. They avoid triggering traditional security alerts.
Such attacks show AI can enable stealthy, widespread intrusions. They spread across entire ecosystems.
AI Agents as Insider Threats
AI agents are now seen as potential insider threats.
These systems operate autonomously. They can bypass traditional access controls.
A 2026 MIT report found AI agents make decisions without human oversight. This increases the risk of unintended or harmful actions.
Organizations must now monitor AI agent behavior in real time. Access logs and actions need constant auditing.
Defensive Measures and Policy Responses
The UK government has set aside $800 million for AI security. This funding supports research, incident response, and public-private efforts.
Anthropic acquired the confidential startup Opaque Systems. This move shows growing focus on AI safety and secure model development.
Anthropic proposed a bill. This reflects rising fears about AI misalignment.
OpenAI Pauses Frontier Training
OpenAI paused its Frontier AI training after a security incident.
The pause is under investigation. Details have not been publicly released.
Reports suggest the incident may involve unauthorized access to internal data portals or training datasets.
OpenAI models have access to data portals and crypto wallets. This raises concerns about data handling and financial exposure.
LiteLLM Compromised in Supply Chain Attack
A supply chain attack on LiteLLM delivered a credential-stealing tool and a backdoor.
This shows AI tools themselves can be exploited. Secure development and supply chain oversight are now essential.
Foundational AI components must undergo rigorous audits before deployment. Vulnerability testing is no longer optional.
What to Watch Next
Experts will monitor:
- AI model transparency and data handling practices.
- Responses to AI-driven supply chain attacks.
- Government actions on AI use in critical infrastructure.
- Enforcement of AI safety measures like misalignment monitoring.
As AI becomes more embedded in digital systems, cybersecurity must evolve. The balance between innovation and risk remains fragile. Continuous scrutiny, ethical oversight, and proactive defense are essential.
Sources & further reading
Featured image: AI / Cybersecurity newsletter. Via original publisher. Image source