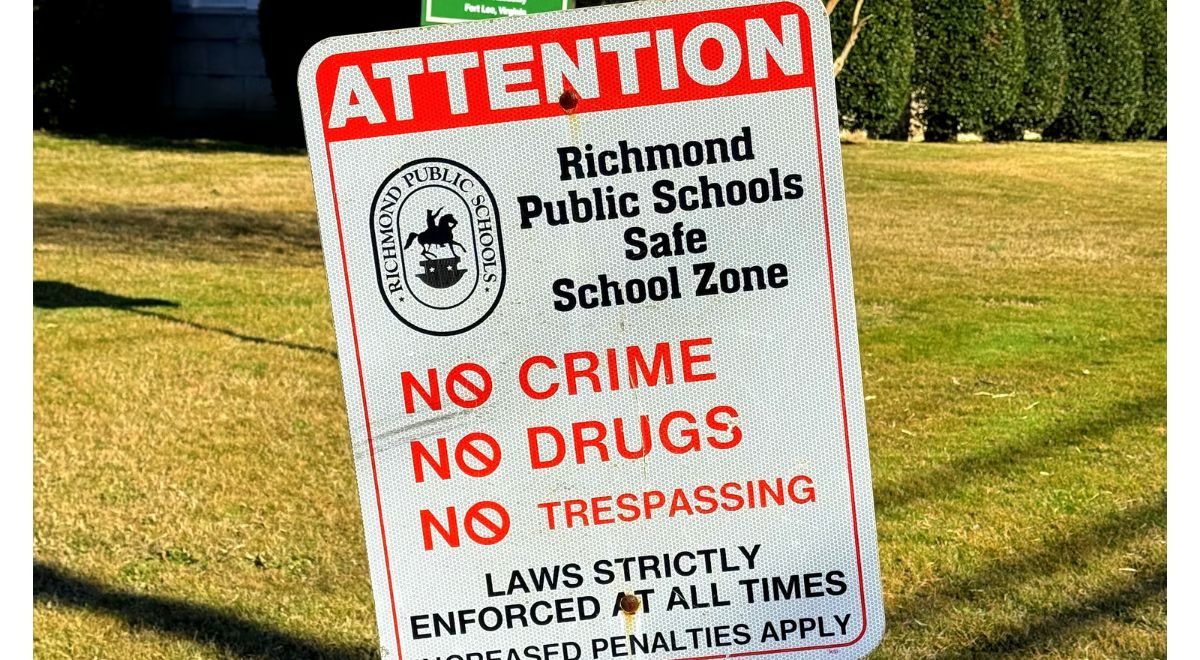
Richmond Public Schools face a ransomware attack that disrupted key digital systems, affecting over 50 schools and 22,000 students.
What Happened
On Wednesday morning, staff discovered threatening messages on district-issued laptops. The messages claimed hackers had breached the network and accessed sensitive data.
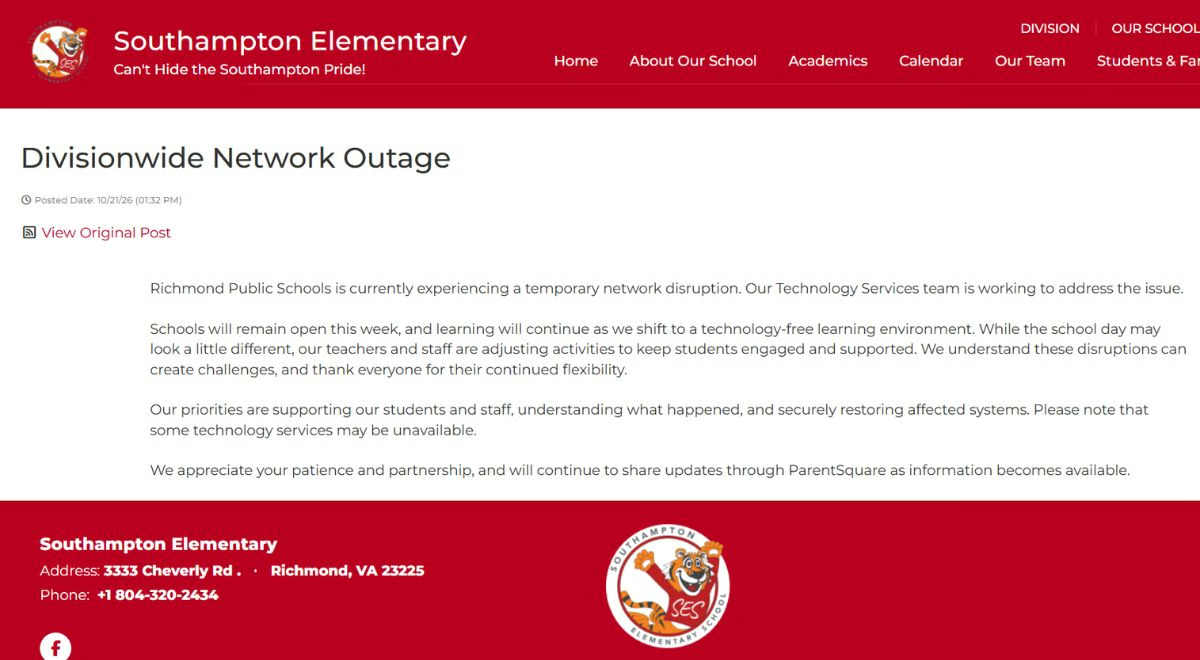
As a precaution, the district shut down its entire network. A public notice was posted on the school website and shared via ParentSquare. A follow-up email confirmed the divisionwide network outage and explained the system failures.
Key Facts
- Teachers lost access to attendance records, student passes, and smart boards. These tools are essential for daily classroom operations.
- Students couldn’t use school Chromebooks or access PowerSchool, a key platform for student records and learning.
- Staff were instructed not to connect to the network or log into devices during the investigation.
- The district has not confirmed any data was stolen, though hackers threaten to publish sensitive student data.
- The ransomware group responsible has not been named. Its motives remain unknown.
- Superintendent Jason Kamras said student safety and physical operations were unaffected. School continued as scheduled.
How the Outage Progressed
At 7:00 a.m. ET, staff received an email advising against logging into any devices or connecting to the network. This was followed by a detailed message later that day.
By midday, officials confirmed the attack impacted Wi-Fi, classroom cameras, and the PowerSchool portal. These systems support both teaching and administrative functions.
What the District Said
Superintendent Jason Kamras called the shutdown a necessary step to secure the system. He said, ‘We understand that these disruptions create challenges for our entire school community. Our priorities are supporting our students and staff, understanding what happened, and restoring affected systems securely.’
He stressed that no student safety risks were present. Teachers adjusted lessons to work around the limitations.
Why It Matters
A network outage in a large public school district can disrupt learning and administrative tasks. This incident shows real vulnerabilities in school IT systems.
With 50 schools and 22,000 students involved, the scale is significant. The threat of student data exposure remains serious—even without confirmed theft.
As schools rely more on digital tools, stronger cybersecurity and faster response plans are urgently needed.
Limitations and Open Questions
The district has not confirmed whether any data was accessed or stolen. This leaves uncertainty about actual data exposure.
No details have been released about the ransomware group or its goals. The attack may be part of a wider trend targeting public institutions.
While classes continued, teachers faced added workloads. The long-term effect on learning is still unknown. Parents and staff are waiting for official updates on the investigation and recovery steps.
What to Watch Next
A formal investigation may begin. The district plans to release a full report in the coming days, covering the timeline, attack nature, and recovery efforts.
Parents and staff should follow official channels. This incident could lead to new cybersecurity policies in public schools, including better monitoring, access controls, and response plans.
For more on this incident, see the original report at Cybernews.
Sources & further reading
Featured image: Hackers knock Richmond schools offline, deface teachers laptops with ransom threats. Via original publisher. Image source