Check Point gateways exploited in cyberattack targeting Israeli organizations
Security researchers have identified a recent cyberattack targeting unpatched Check Point Security Gateways. The attack began on October 30, 2026, and primarily affected Israeli organizations.
What Happened
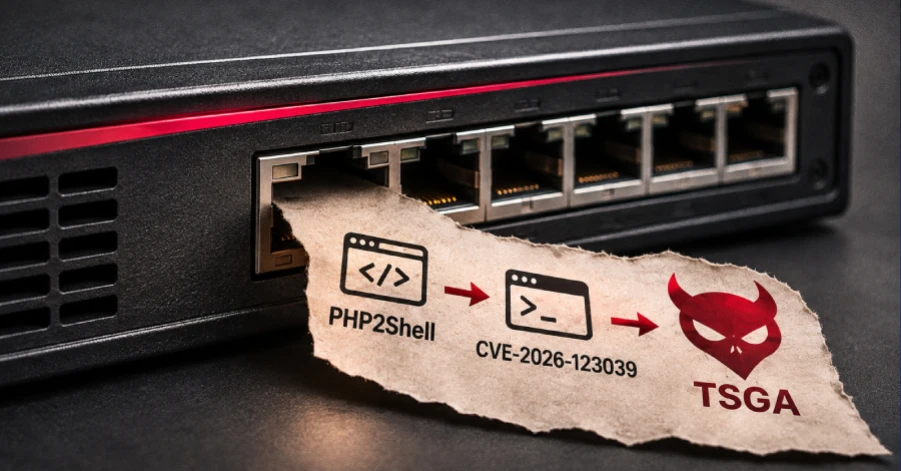
Attackers used a combination of vulnerabilities to gain access to Check Point gateways. The initial access was achieved through a flaw known as PHP2Shell, which allows remote code execution.
After gaining initial access, threat actors exploited a previously reported local privilege escalation flaw in Gaia OS—the operating system that manages Check Point gateways. This allowed them to escalate privileges and gain deeper control of the system.
Once inside, they deployed a backdoor named TSGA. This backdoor enables remote access and command execution, allowing attackers to maintain persistent access to the network.
As part of the attack, attackers also attempted to wipe ESXi files. These files are critical for virtual machine management in data centers. Their removal could disrupt operations and lead to service outages.
Key Facts
- The attack began on October 30, 2026.
- Targeted organizations in Israel.
- Used PHP2Shell to gain initial access.
- Exploited a local privilege escalation flaw in Gaia OS.
- Deployed a backdoor named TSGA.
- Attempted to delete ESXi files to disrupt operations.
Check Point has confirmed the activity and issued a public alert. The company has not yet released a full technical report, but its security team has been investigating the incident.
Background: How the Vulnerabilities Work
PHP2Shell is a known vulnerability in PHP-based web applications. It allows attackers to execute arbitrary code on a server by uploading a malicious script. If a system uses PHP scripts without proper validation or access controls, this flaw can be exploited.
The Gaia OS privilege escalation flaw enables an attacker with limited access to gain full administrative rights. This is particularly dangerous in network gateways, where access control is critical.
ESXi is the hypervisor used in many enterprise data centers. Wiping its files would prevent virtual machines from booting, potentially leading to service disruption.
Why It Matters
This attack demonstrates how a combination of known vulnerabilities can be chained together to achieve significant compromise. Even if one vulnerability is patched, the presence of others can still allow attackers to gain access.
Organizations using Check Point gateways must ensure all systems are updated. The attack shows that outdated software remains a major risk, especially in critical infrastructure.
Check Point has issued a security advisory. It recommends immediate patching of all gateways and reviewing configurations for known vulnerabilities.
Limitations and Open Questions
The source does not confirm whether the attack was limited to Israel or if it has expanded to other regions. There is no public evidence of broader global targeting.
It is unclear whether the TSGA backdoor was used to exfiltrate data or only to maintain access. The source does not specify data theft or lateral movement.
There is no mention of whether the attack was part of a larger campaign or a single isolated incident. The timeline and scope remain under investigation.
Check Point has not confirmed whether the vulnerability in Gaia OS was previously disclosed or if it was exploited in a prior incident.
What to Watch Next
Security teams should monitor for signs of similar attacks on other network gateways. The combination of PHP2Shell and privilege escalation flaws could be reused in other systems.
Organizations should review their patch management processes. Delayed updates are a common vector for such attacks.
Check Point’s advisory on the PHP2Shell vulnerability is available at PHP2Shell Vulnerability: Early Exploitation and Security Risks.
For a detailed account of the attack, refer to the original report at The Hacker News.
Sources & further reading
Featured image: original publisher image. Via original publisher. Image source