At a recent event, Microsoft CEO Satya Nadella highlighted a growing concern in digital infrastructure: many critical systems remain unpatchable due to outdated firmware.
Unpatchable Systems in Critical Infrastructure
Nadella pointed out that a significant portion of America’s infrastructure—such as chillers and HVAC systems—runs on firmware that cannot be updated.
These systems are now connected to the internet, making them accessible and vulnerable. He emphasized that this connectivity has created new risks, even as the systems themselves were never designed with modern cybersecurity in mind.
‘There is a lot of stuff in our critical infrastructure that’s unpatchable,’ Nadella said. ‘Think about all the firmware and the chillers and the HVAC systems everywhere else. So all of that, by the way, they’re on the internet.’
Why This Matters
As more devices become internet-connected, the attack surface expands. Legacy systems that were once isolated are now part of a global network. This means a single vulnerability could affect multiple sectors—from power grids to transportation.
AI-aided tools now scan vast networks quickly to find exploitable flaws. One attendee noted these tools can detect firmware-level vulnerabilities in minutes—far faster than manual audits.
Nadella said companies used to have time to test patches and understand risks before deployment. Now, patches must go from available to live in production almost instantly—because they’re being exploited in the wild.
Recent Outages and Their Context
Recent large-scale outages—including Microsoft Outlook, the NSA, and Apple—have raised concerns about cyberattacks. Officials have not confirmed these as attacks.
Nadella said the Outlook outage came from a ‘latent bug’ that triggered a ‘perfect storm’ of failures. The company launched an incident response and will apply lessons to improve both system design and operations.
He also noted that transportation systems have vast software exposure—but none of it can be patched. This gap undermines real-time threat detection and system resilience.
What This Means for Security
Traditional patching cycles—once lasting weeks—no longer work. AI-powered tools now find vulnerabilities faster than any human team can respond.
Companies face a paradox: they must patch instantly to prevent exploitation, but doing so can destabilize systems not built for real-time updates.
One analyst said the current software model clashes with modern cyber threats. ‘The moment a vulnerability is detected, it’s already being used,’ the analyst said. ‘AI can now automate the attack chain from discovery to execution in under an hour.’
Nadella stressed the need to modernize infrastructure and assess real-time detection and defense capabilities. ‘We’ll have to really modernize for sure,’ he said. ‘And then we will have to assess what the threat vector looks like, what our own ability to both detect and then defend in real time looks like.’
Limitations and Open Questions
Nadella’s remarks highlight a major risk—but do not offer a solution. The issue of unpatchable systems remains unaddressed in policy or industry standards.
There is no known timeline for replacing legacy firmware in critical infrastructure. Many systems were installed decades ago and have no official support path.
AI’s role in actual cyberattacks remains unproven in public reports. While AI tools are used in testing, no evidence shows AI-powered attacks caused major outages.
Still, the growing use of AI in both attack and defense suggests the threat landscape is evolving rapidly—without clear safeguards.
As more systems connect, securing them will only grow harder. The current infrastructure may not be ready for the full scope of digital-age risks.
For more on AI and cybersecurity, see the original source at TechCrunch.
Sources & further reading
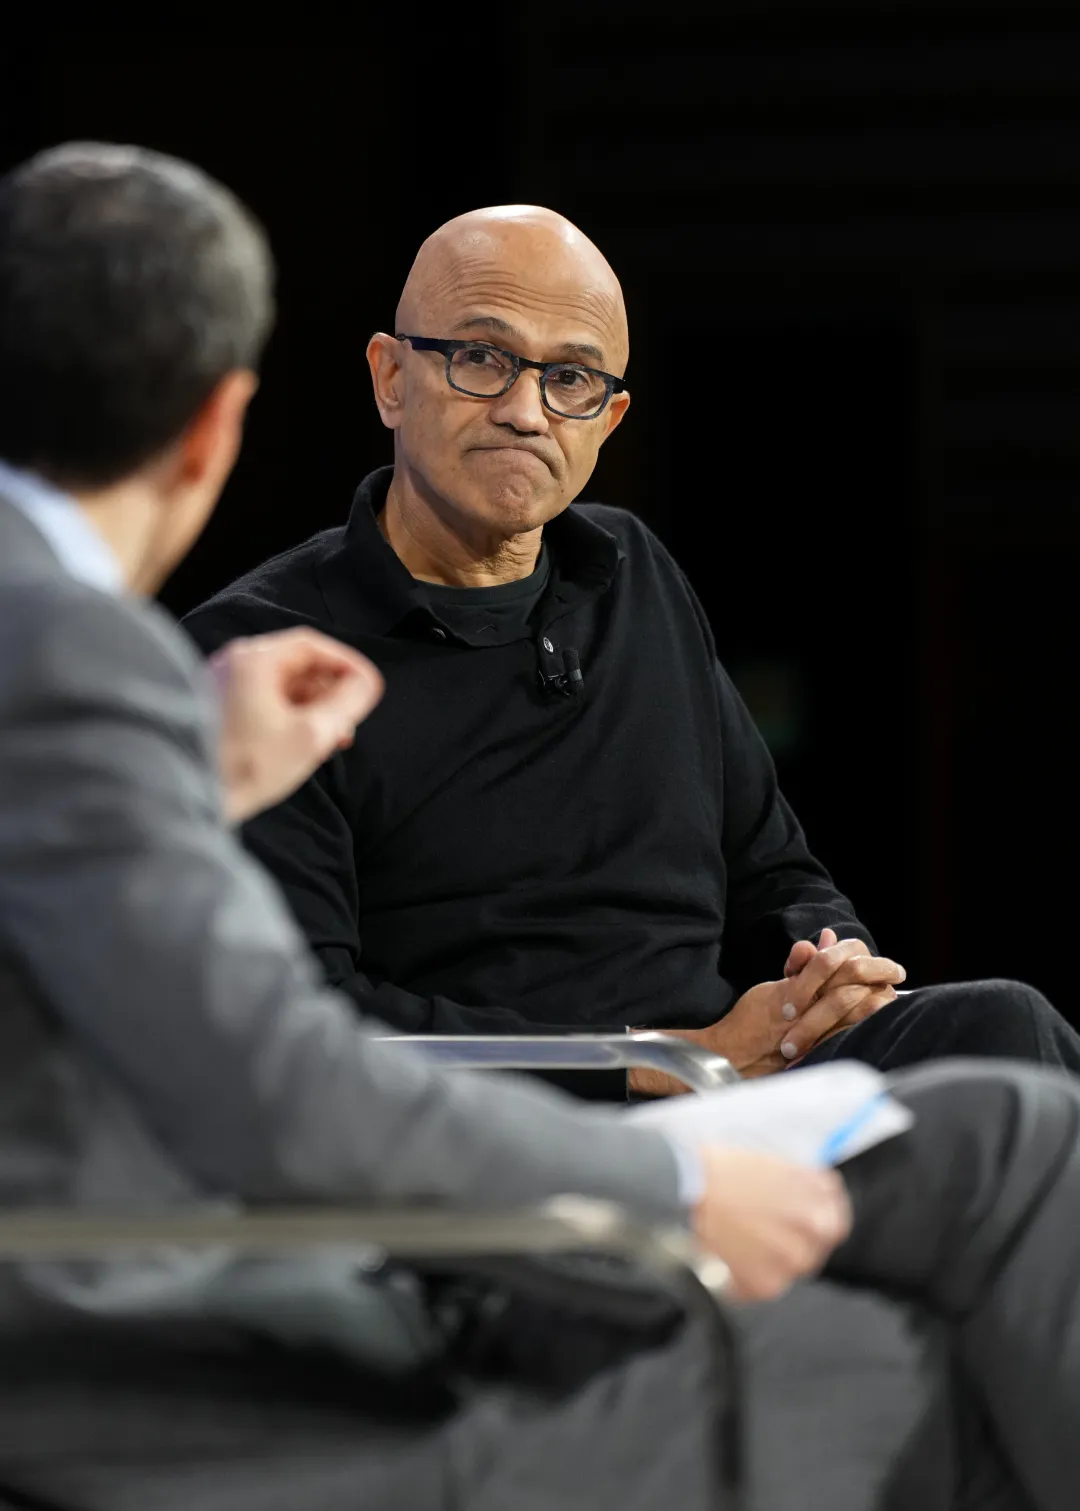
Featured image: NEW YORK, NEW YORK – NOVEMBER 18: Satya Nadella speaks onstage during the NY Times Dealbook Summit at Jazz at Lincoln Center on November 18, 2026 in New York City. (Photo by Adam Gray/Getty Images for The New York Times). Via original publisher. Image source